CloudFormation + GitHub Actions — Plan-Letting Platform
Wrote a CloudFormation template that provisions a VPC with public and private subnets, routing, a security group and a bootstrapped Apache web server, then built a GitHub Actions workflow that assumes AWS credentials from repository secrets and runs aws cloudformation deploy. This is v1 of a multi-cloud design that will add an ALB, Auto Scaling, RDS, VPC peering and Azure-hosted HLS video delivery.
Business value
For a hospitality platform that needs repeatable environments, this replaces console clicking with a version-controlled CloudFormation template that a GitHub Actions workflow deploys on demand. Every change is reviewable in a pull request and re-running the pipeline updates the stack in place, so environments stop drifting and rollbacks are a git revert away.
The problem
The module brief asks for a hospitality booking platform whose infrastructure is fully automated rather than built by hand, with a clear path from a single trial stack to a modular, multi-tier, multi-cloud architecture. The first milestone was to prove the automation end to end: infrastructure defined in a template, deployed from a clean CI runner with nothing but the repository and secrets, and verified by a working public web server.
What I built
- 01
Defined the network in CloudFormation: a 172.18.0.0/16 VPC with DNS support, a private subnet in one AZ and a public subnet in another, using !GetAZs and !Select so the template stays region-agnostic.
- 02
Attached an Internet Gateway, created a public route table with a 0.0.0.0/0 default route and associated it with the public subnet, using DependsOn where CloudFormation cannot infer ordering.
- 03
Added a security group permitting HTTP and HTTPS inbound and an EC2 instance whose user-data installs and enables Apache on first boot.
- 04
Exposed the instance public IP as a stack output so the pipeline can print the endpoint after every deploy.
- 05
Built a workflow_dispatch GitHub Actions pipeline that checks out the repo, configures AWS credentials from secrets, runs aws cloudformation deploy with CAPABILITY_NAMED_IAM, then describes the stack outputs.
- 06
Documented the known limitations of v1 (single monolithic stack, publicly exposed web tier) and the roadmap: modular stacks, an internet-facing ALB in front of a private Auto Scaling Group, RDS with a read replica in a peered VPC, a management instance, and Azure Blob Storage behind Front Door for HLS video.
Project stages
01 / 02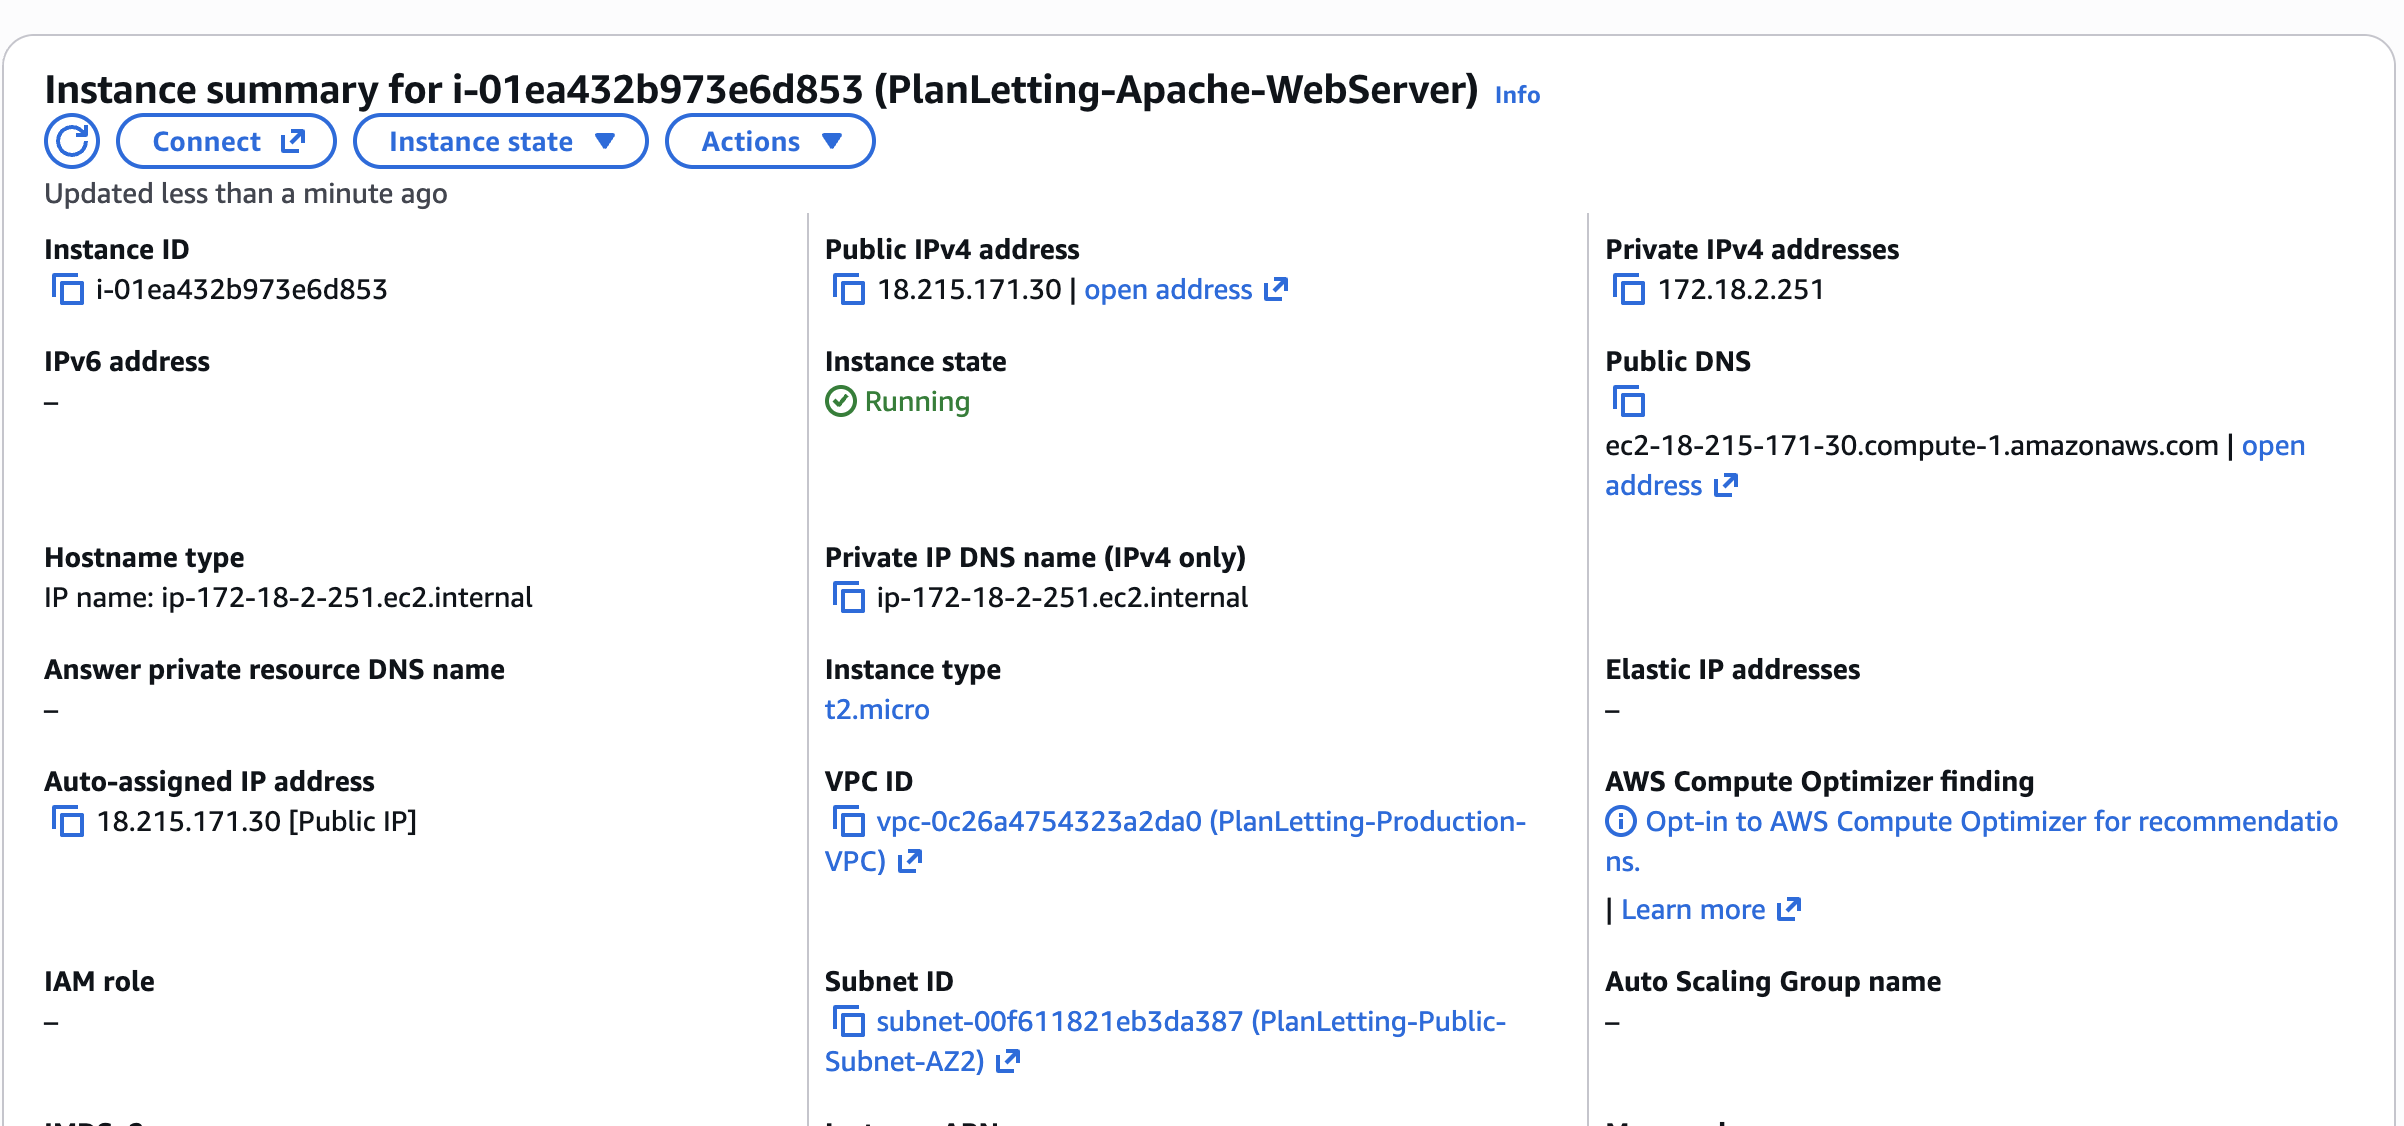
Stage 01 — the PlanLetting-Apache-WebServer instance created by the stack, running in the PlanLetting-Production-VPC public subnet with a public IPv4 address.